Vulnerability
From Arbitrary File Read to Shell: Yet Another RCE in Telerik
A vulnerability in Telerik UI for ASP.NET AJAX led to an arbitrary file read via RadImageEditor's image cache. Leaking web.config turned it into RCE.
Stay informed with the latest research, security insights and updates from the Tanto Security team.
Vulnerability
A vulnerability in Telerik UI for ASP.NET AJAX led to an arbitrary file read via RadImageEditor's image cache. Leaking web.config turned it into RCE.
Vulnerability
How a sacrificial block turned a decrypt-only padding oracle into a forgery, and the forgery into unauthenticated RCE.
Vulnerability
Four bugs in Apryse WebViewer Server, from reading every user’s documents to unauthenticated RCE, and an auth bypass that remains unfixed.
Vulnerability
The root login that wasn’t really root on PUSR’s USR-G806AU, and the real superuser’s password baked into its firmware all along.
TantoSec
Our 2025 in review: new starters, touching grass, talks from CrikeyCon to Kawaiicon, CTFs, and bullying a printer by voice.
Security Assessment
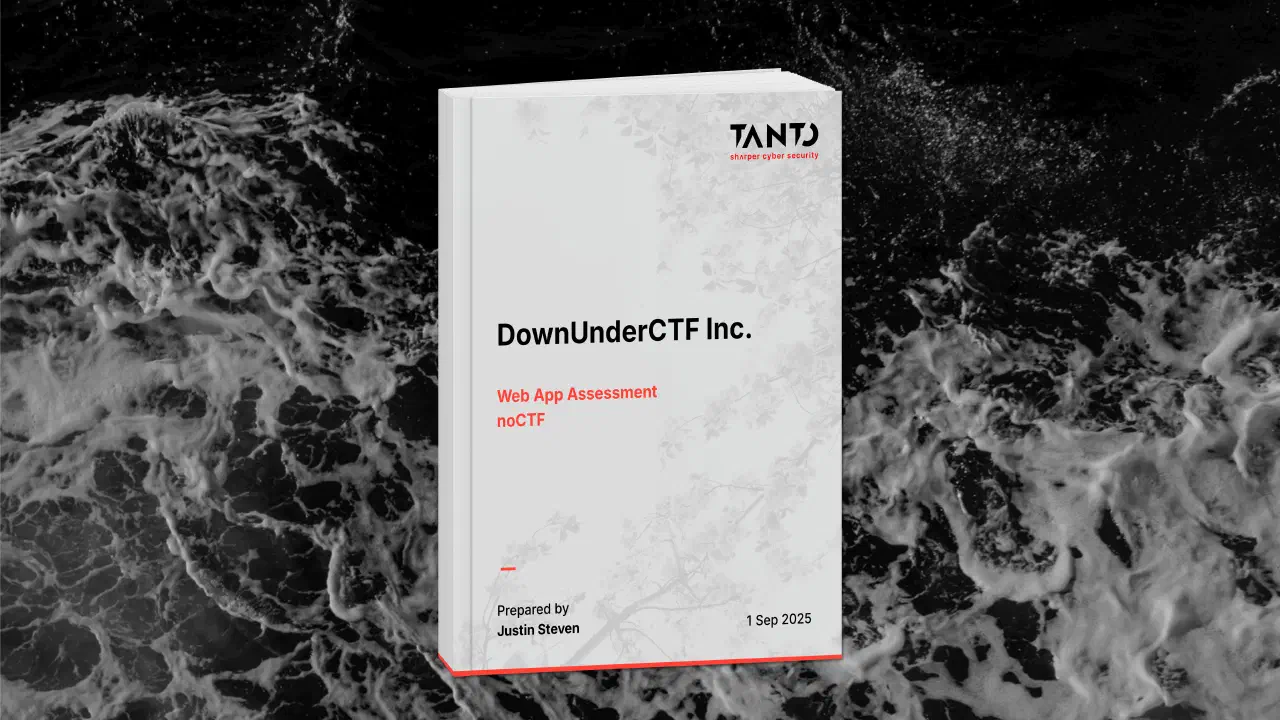
We gave noCTF a free pentest, and we’re giving the report away.
Phishing
Forged headers, suppressed safety tips and malformed addresses could let an external sender pass as your CEO in Outlook.
Vulnerability
Template injection in Kong’s Insomnia API client leads to remote command execution that survived three attempted fixes.
Vulnerability
A poisoned password reset, a page editor who can read the admin’s account file, and a scheduler that writes a web shell.